Why a DPO Alone Isn't Enough Without a DPMS
There's a common pattern that plays out inside a lot of growing companies. Someone in leadership realises the organisation handles a meaningful amount of personal data, whether that's customer records, employee files, patient information, or tenant details. A decision gets made to appoint a Data Protection Officer, either by hiring someone into the role or assigning it to an existing staff member. A privacy notice gets published on the website. And then, quietly, everyone assumes the job is done.
It isn't. Not because the DPO isn't doing their job, but because appointing a person to oversee something is a completely different thing from having a system that lets that oversight actually happen in a way anyone can see, trust, and rely on later.
What a DPO is actually supposed to be watching
Personal data protection today covers a lot more ground than a privacy notice ever could. An organisation is expected to know what personal data it collects, why it collects it, where that data physically or digitally lives, who inside the company can access it, how long it gets kept before it's deleted, and what happens the moment something goes wrong, whether that's a person asking what data you hold on them or a genuine security incident.
A Data Protection Officer's job is to watch over all of that. They're the person who's supposed to know the answers, or know how to find them quickly, when a regulator, a customer, or an internal audit asks. That's a real and necessary role. But watching over something and having proof of what happened are two different jobs, and a DPO can only do the first one well if the second one is already being handled somewhere.
The gap nobody notices until it matters
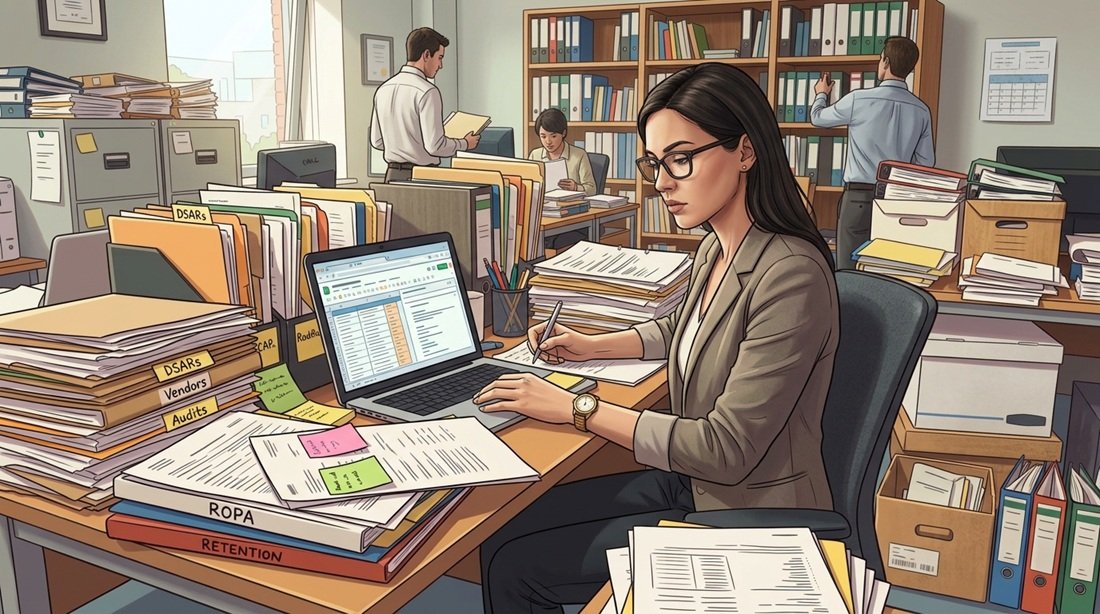
Here's where things usually fall apart. A DPO gets appointed, and their actual working tools end up being a mix of email threads, shared drives, spreadsheets somebody built during onboarding, and whatever informal habits the team has picked up. There's no single place that shows, at a glance, which data subject requests are still open, which vendor contracts still need a privacy review, or which department hasn't confirmed how long they're keeping old records.
None of this is usually anyone's fault. It happens because oversight, on its own, doesn't come with a place to live. A DPO can genuinely be doing good work, reviewing things, raising flags, following up, and still have almost nothing to show for it if someone asks for evidence six months later. And evidence is exactly what tends to matter most, whether that's for an internal audit, a customer's due diligence questionnaire, or a regulator's inquiry.
This is the part that catches organisations off guard. It's rarely the absence of a DPO that causes problems. It's the absence of a system that would have let that DPO's work be tracked, proven, and repeated consistently across every department, every request, and every incident.
What a proper system actually gives you
This is what a Data Protection Management System is for. Rather than replacing the DPO, it gives the DPO, and everyone else touching personal data across the organisation, a structured place to actually do the work that oversight requires.
A few concrete examples make this easier to picture. When a customer, employee, or any other individual asks what personal data you hold on them, or asks you to correct or delete it, that request needs to be tracked from the moment it arrives: who owns it, whether the requester's identity has been verified, what the deadline is, what evidence supports the response, and when it was actually closed. Without a system, that tracking lives in someone's inbox, and inboxes are a terrible place to prove anything happened correctly under pressure.
The same is true when something goes wrong. A privacy incident, big or small, needs its key details recorded, its investigation tracked, its corrective actions documented, and its resolution clearly closed out. Trying to reconstruct that after the fact, from memory and scattered messages, is exactly the situation nobody wants to be in when a regulator or a customer is asking what happened and what you did about it.
It extends outward too. Most organisations don't just handle personal data themselves, they hand pieces of it to vendors and data processors: payment providers, cloud storage, marketing tools, HR platforms. Each of those relationships carries its own risk, and without a structured record of what each vendor does with your data, what their contractual status is, and when they were last reviewed, that risk sits invisible until something forces it into view.
And underneath all of this sits documentation. Not documentation for its own sake, but a centralised, organised trail of records and evidence that means an internal review, a management report, or an external audit can actually be answered with real proof instead of a scramble to reconstruct what happened.
Why this changes what compliance actually looks like day to day
Put all of this together and something shifts. Compliance stops being a folder of documents that gets dusted off once a year before an audit, and becomes something closer to an ongoing operating rhythm. Requests get logged the moment they arrive instead of sitting in someone's inbox. Incidents get a clear, repeatable process instead of an improvised scramble. Vendor risk gets reviewed on a schedule instead of being forgotten until a contract renewal forces the question.
None of this requires the DPO to work harder. If anything, it means the DPO stops being the single point of memory for the entire organisation's data protection activity, which is an exhausting and fragile position for any one person to hold. Instead, the system carries the memory, and the DPO's real job, watching, judging, and advising, becomes something they can actually focus on.
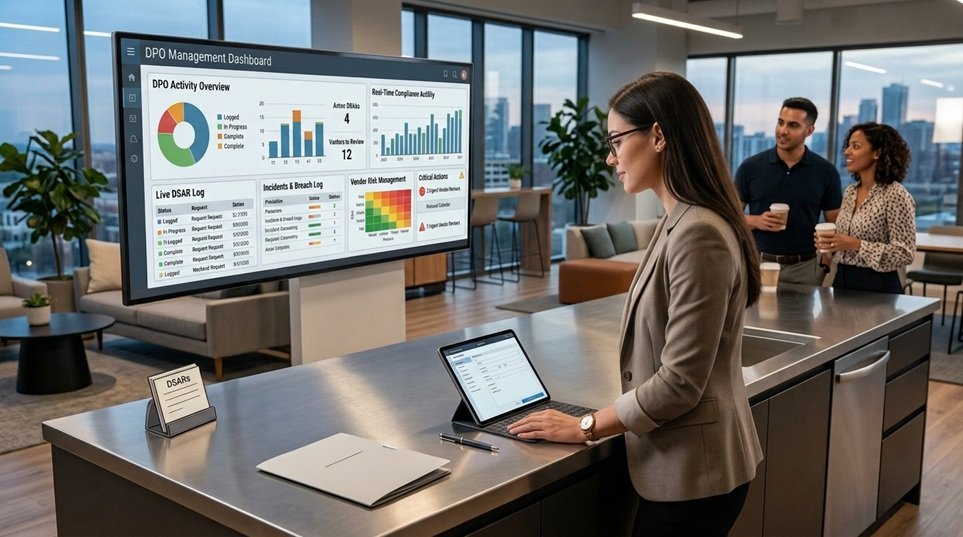
There's also a quieter shift that matters just as much: visibility for the people running the business. A management dashboard that shows real-time compliance activity, outstanding actions, and risk areas turns data protection from a topic that only comes up when something goes wrong into something leadership can actually see and factor into decisions, the same way they'd look at sales numbers or operational metrics.
Who actually needs to be thinking about this
This isn't a concern reserved for large enterprises with dedicated legal departments. Any organisation that regularly touches customer, employee, patient, tenant, member, or platform user data is carrying this responsibility already, whether or not anyone's built a system around it yet. That covers a lot of ground: SaaS companies, e-commerce businesses, HR and recruitment firms, healthcare and wellness providers, rental and subscription businesses, financial service support companies, property and community management operators, and any multi-branch service business juggling data across several locations.
What these businesses tend to have in common isn't size, it's growth. The moment a company starts handling personal data across more than a handful of people, more than one department, or more than one system, informal tracking stops being enough, whether or not anyone's noticed yet.
Moving from a document on a shelf to a system that actually runs
The honest reality is that a DPO, no matter how capable, is working against the odds if their only tools are scattered documents and personal memory. The role was never meant to carry that weight alone. What changes the equation isn't replacing the person, it's giving them, and the rest of the organisation, a structured system where compliance work actually gets recorded, tracked, and proven as it happens, not reconstructed after the fact when someone finally asks.
If your organisation has a DPO, or is about to appoint one, and their day-to-day still runs on spreadsheets, shared folders, and good intentions, that's worth a closer look. The gap between having someone responsible and having something that shows what that responsibility actually produced is exactly where most compliance problems quietly grow.